# Overview
Prventi is a managed Security Awareness Training (SAT) platform that lets you identify your most vulnerable employees and provide targeted training to enhance their cybersecurity awareness and skills.
## Quick links
{% content-ref url="/pages/7O8akWmvS9OvNl0N2nCH" %}
[Getting started](/guides/getting-started)
{% endcontent-ref %}
## Get Started for Teams
We've put together some helpful guides for you to get setup with our product quickly and easily.
{% content-ref url="/pages/OKbbCgvQFNIKm3wBq8DX" %}
[Allowlisting Prventi email servers](/guides/getting-started/allowlisting-prventi-email-servers)
{% endcontent-ref %}
# Cyber security awareness training
### **What is** Cyber **Security Awareness Training?**
Security Awareness Training is a structured program designed to educate employees about the risks related to information technology, cyber threats, and best practices to defend against them. In today's digital world, cyber threats lurk around every corner, making everyone a potential target. The most effective line of defence against these threats isn't just technology—it's well-informed individuals.
### **Why is** Cyber **Security Awareness Training Important?**
1. **Human Element:** Cyber threats often target the human element. A single click on a malicious link by an unsuspecting employee can lead to a security breach.
2. **Evolving Threats:** Cyber threats are continually evolving. Regular training ensures employees stay updated on the latest threats and response measures.
3. **Regulatory Compliance:** Many industries have regulations that mandate periodic security training for staff.
4. **Protect Organizational Reputation:** A security breach can lead to financial losses and a damaged reputation. Training employees reduces the risk of a breach stemming from human error.
### **Prventi's Approach to** Cyber **Security Awareness Training**
At Prventi, we understand the dynamic nature of today's business environment and the constraints on employees' time. Hence, we've adopted a mobile-first, bite-sized training approach. Here's why it stands out:
1. **Mobile-First Design:** In an era where smartphones are ubiquitous, our training modules are designed to be easily accessible on mobile devices. Whether employees are on-the-go or taking a short break, they can engage in training without the need for a desktop setup.
2. **Bite-Sized Learning:** Information retention is enhanced when training is delivered in concise, focused segments. Our modules are designed to impart key knowledge in short, engaging bursts, ensuring employees grasp and retain vital information without feeling overwhelmed.
3. **Interactive Content:** Prventi's training isn't just about passively consuming information. We integrate quizzes, simulations, and interactive scenarios, making learning engaging and practical.
4. **Real-time Feedback:** As users progress through modules, they receive immediate feedback on their performance, helping to reinforce learning and identify areas that might require further attention.
***
By addressing the unique challenges organisations face in the digital age, Prventi's Security Awareness Training offers a robust, efficient, and user-friendly solution to bolstering employees' cyber resilience.
# Phishing simulation tests
### **What are Phishing Simulation Tests?**
Phishing Simulation Tests are controlled, benign attempts to mimic real-life phishing scenarios to test and educate employees on their ability to recognize and respond to malicious cyber threats. By simulating these threats in a safe environment, organizations can identify areas of vulnerability and take proactive steps to address them before a real threat emerges.
### **Why are Phishing Simulation Tests Important?**
1. **Real-World Application:** It's one thing to be told about threats; it's another to experience them. Simulated tests give employees hands-on experience with phishing tactics without the associated risks.
2. **Vulnerability Assessment:** Organizations can identify which employees are most susceptible to phishing attempts, allowing for targeted training and mitigation strategies.
3. **Reinforcement of Training:** Phishing simulations reinforce security awareness training by placing knowledge into practice, solidifying the learning experience.
4. **Metrics and Reporting:** By assessing the results of the simulations, organizations gain valuable insights into their cybersecurity posture, helping guide future training and security policies.
### **Prventi's Approach to Phishing Simulation Tests**
Prventi offers a comprehensive, tailored experience for organizations aiming to improve their cybersecurity readiness:
1. **Variety of Scenarios:** Our platform contains a wide array of phishing scenarios, imitating the latest techniques used by cybercriminals. This ensures employees are exposed to a broad spectrum of potential threats.
2. **Automated Campaigns:** Prventi allows organizations to schedule and automate phishing tests, ensuring regular assessment without manual intervention.
3. **Instant Feedback:** If an employee falls for a simulated phishing attempt, they receive immediate feedback with educational pointers, turning a potential vulnerability into a learning opportunity.
4. **Detailed Reporting:** Post-simulation, Prventi provides in-depth analysis and metrics, highlighting areas of concern and showcasing improvement over time. This data-driven approach aids organizations in refining their cybersecurity strategies.
***
Prventi's Phishing Simulation Tests are more than just a testing tool. They're an educational instrument, a mirror reflecting an organization's cybersecurity health, and a guide for future improvements. With a combination of real-world scenarios, immediate feedback, and in-depth analytics, Prventi empowers organizations to fortify their defenses against one of the most prevalent cyber threats today.
# Identity protection monitoring
In an era where our digital footprints are as significant as our physical ones, safeguarding personal and professional identities against theft and misuse is paramount. Prventi's Identity Protection Monitoring is your vigilant digital guardian, ensuring that your sensitive information remains secure.
#### What Is Identity Protection Monitoring?
Our Identity Protection Monitoring service is a proactive surveillance tool that scours the darkest corners of the internet, including the places where data breaches often lead to exposed personal data. It's designed to detect if your information – such as email addresses, passwords, and personal identification numbers – appears in any compromised databases or public leaks.
#### Why Is This Important?
The early detection of your data in a breach is critical. It can be the difference between a quick, protective response and the disastrous consequences of identity theft. Our monitoring allows you to:
* **Act Fast:** Receive immediate alerts if your data is compromised, giving you the chance to change passwords and secure accounts before any damage can be done.
* **Stay Informed:** Understand which of your accounts or data points has been exposed, so you can make informed decisions about your next steps.
* **Reduce Risk:** Learn about the implications of password reuse and get guidance on creating strong, unique passwords for every account.
#### How Does It Help?
* **Continual Monitoring:** Prventi keeps an unblinking eye on a myriad of sources where information may be leaked or exposed.
* **Intelligent Alerts:** You'll receive timely, clear notifications about any incidents involving your data, so there's no delay in your response.
* **Educational Resources:** Beyond alerts, Prventi provides advice and resources to help you understand and react to these incidents, including best practices for securing your digital identity.
#### The Prventi Advantage
* **Comprehensive Coverage:** Our monitoring is not limited to the surface web. We extend our reach to the deep web and darknet, where data breaches often surface first.
* **User-Friendly Interface:** Our platform is designed for ease of use. You don’t need to be a tech expert to navigate through the alerts or understand the implications.
* **Actionable Insights:** When we detect your data in a breach, we don’t just inform you—we give you the actionable steps
# Getting started
1. [Login or create a new account](/guides/getting-started/login-or-create-a-new-account)
2. [Create an organisation](/guides/getting-started/create-an-organisation)
3. [Add learners](/guides/getting-started/add-learners)
4. [Verify domain ownership](/guides/getting-started/verify-domain-ownership)
5. [Allowlist Prventi email servers](/guides/getting-started/allowlisting-prventi-email-servers)
6. [Send a delivery test email](/guides/getting-started/send-a-delivery-test-email)
7. [Start a baseline phishing campaign](/guides/getting-started/start-a-baseline-phishing-campaign)
{% content-ref url="/pages/OKbbCgvQFNIKm3wBq8DX" %}
[Allowlisting Prventi email servers](/guides/getting-started/allowlisting-prventi-email-servers)
{% endcontent-ref %}
# Login or create a new account
To get started with Prventi, create a free account on Prventi.com and verify the linked email address.
Every person who uses Prventi needs an account to sign-in to access the services. This account is the identity linked to the services and has a username and profile.
## Create a new account
1. Navigate to .
2. Click **Try it for free.**
3. Click on the preferred account creation method: [**Continue with Apple**](#continue-with-apple), [**Continue with Google**](#continue-with-google) or [**Continue with an email address**](#continue-with-an-email-address)**.**
### **Continue with Apple**
1. Click on "Continue with Apple" and follow the prompts.
{% hint style="info" %}
For more information about Sign in with Apple see
{% endhint %}
### **Continue with Google**
1. Click on "Continue with Google" and follow the prompts.
{% hint style="info" %}
For more information about Sign in with Google see
{% endhint %}
### **Continue with an email address**
1. Type in a valid email address.
2. Click **Continue**.
3. Check your inbox - An activation link is sent to the email address entered. (Check the spam folder if you don't see it in the inbox)
4. Click on the **Sign in** button in the email sent from .
5. Click on the **Continue to your account** button.
6. Follow the promts to complete account creation.
{% hint style="warning" %}
The activation link will expire after 15 mins. Do not forward this email to prevent unauthorise acess to the account.
{% endhint %}
# Create an organisation
To get started using Prventi in an organisation an organisation account is needed. A Prventi organisation account is linked to at least one Prventi personal account.
The only pre-requisite to use an organisation account is the ability to [verify domain ownership](/guides/getting-started/verify-domain-ownership).
### Create an organisation
1. Type in the organisation name.
2. Type in the organisation's website URL.
3. Select the country where the organisation is based.
4. Click **Continue**.
The organisation is now created on Prventi.
# Add learners
Before you can start your Baseline Phishing Campaign, you will need to add or import your team members as learners into your organization on Prventi.
[Automatic learner provisioning](/guides/getting-started/add-learners/automatic-learner-provisioning)
# Automatic learner provisioning
[Google Workspace user provisioning](/guides/getting-started/add-learners/automatic-learner-provisioning/google-workspace-user-provisioning)
[Microsoft Entra ID automatic user provisioning](/guides/getting-started/add-learners/automatic-learner-provisioning/microsoft-entra-id-automatic-user-provisioning)
# Microsoft Entra ID automatic user provisioning
This guide will walk you through the steps to configure automated provisioning for Prventi using Microsoft Entra, formerly known as Azure Active Directory.
{% hint style="info" %}
Before you start, make sure you have generated your SCIM access token.
{% endhint %}
{% hint style="info" %}
Prventi currently does not support SCIM Group syncing.
{% endhint %}
### Register Prventi in Microsoft Entra
1. Sign into your [Microsoft Entra](https://entra.microsoft.com) admin center
2. In the left pane, expand `Applications`
3. Select `Enterprise Applications`
4. Select `+ New application`
5. Select `+ Create your own application`
6. Enter a name for your application, you can use `Prventi SCIM`
7. Make sure `Integrate any other application you don't find in the gallery (Non-gallery)` is selected
8. Select `Create` to submit the form
### Configure provisioning
1. In the app that you have just created, find and select `Provisioning` in the left pane under `Manage`
2. Now do the same again
3. Select `Automatic` from the `Provisioning Mode` dropdown list
4. Enter [https://app.prventi.com/scim\_v2](https://prventi.com/scim_v2) in the `Tenant URL` field
5. Enter your Prventi SCIM token in the `Secret Token` field
6. Select `Test Connection` to make sure that your connection is working
7. Select `Save` to commit your configuration
### Disable Groups provisioning
1. Once saved, expand the mappings option in `Provisioning`
2. Select `Provision Active Directory Groups`
3. Set `Enabled` to `No` and save
### Add Users and Groups
1. Select `Users and Groups` under `Manage` in the left pane
2. Add the users and groups that you want to sync to Prventi
3. Save
### Start Provisioning
1. Navigate back to the root of your app
2. Select `Provisioning` under `Manage` in the left pane
3. Select `Start Provisioning`
# Google Workspace user provisioning
Coming soon
# Verify domain ownership
Before you launch your organisation's baseline phishing campaign, the first and most crucial step is to verify the ownership of your domain. This step ensures that Prventi can securely and legitimately deliver phishing simulation emails to the email addresses under your organisation's control.
#### Why Verify Your Domain?
* **Security and Legitimacy:** Domain verification is a security measure that confirms you have authorized control over the domain. This prevents misuse of the platform and ensures that phishing simulations are conducted legitimately and safely.
* **Effective Campaign Delivery:** Verified domains ensure that our phishing simulation emails reach your employees without being blocked by spam filters or other email security systems.
* **Compliance:** Verifying your domain aligns with best practices for legal and ethical phishing simulations, ensuring compliance with various cybersecurity regulations.
#### Step-by-Step Guide to Domain Verification
1. **Access Domain Verification Section:**
* Log in to your Prventi account.
* Navigate to the ‘Domain Verification’ section in your dashboard.
2. **Enter Your Domain:**
* Enter the domain name(s) you wish to use for phishing simulations.
3. **Verify Ownership:**
* Prventi will provide you with a unique verification record.
* Add this record to your domain's DNS (Domain Name System) settings. This process may vary depending on your domain registrar or hosting service. Typically, you will need to access your DNS management interface to add the provided record.
4. **Complete Verification:**
* Once the DNS record has been added, return to Prventi and confirm the completion of this step.
* Prventi will automatically check the DNS record for verification. This process can take up to 48 hours.
5. **Verification Confirmation:**
* You will receive a confirmation email once your domain has been successfully verified.
* If there are issues or delays beyond 48 hours, please contact Prventi support for assistance.
#### Need Help?
If you encounter any challenges during the domain verification process or have questions about modifying your DNS settings, our support team is here to assist you. [Contact our support](https://www.prventi.com/support) for guidance and support.
Thank you for taking this important step in setting up your organization on Prventi. Once your domain is verified, you're all set to launch your baseline phishing campaign and strengthen your organisation's defence against cyber threats.
# Allowlisting Prventi email servers
Phishing attack simulations allowlist and configuration settings.
To ensure that Prventi's phishing simulation emails reach their intended recipients without being blocked by spam and phishing filters, it is essential for receiving email servers to allowlist Prventi's mail servers. Allowlisting helps establish a trusted connection between the sender and recipient, allowing our simulated phishing emails to bypass filtering mechanisms and provide an effective training experience for your team. By following the allowlisting instructions provided in our help documentation, you can ensure a seamless and reliable delivery of Prventi's phishing simulations, helping your organization improve its overall security awareness.
{% content-ref url="/pages/Ei7NysQDd7sMWwrRQY8L" %}
[Google Workspace Allowlisting](/guides/getting-started/allowlisting-prventi-email-servers/google-workspace-allowlisting)
{% endcontent-ref %}
{% content-ref url="/pages/sKuUrIX6QPj13JpwvbwN" %}
[Microsoft Office 365 Allowlisting](/guides/getting-started/allowlisting-prventi-email-servers/microsoft-office-365-allowlisting)
{% endcontent-ref %}
{% content-ref url="/pages/5Ct9ec3dvMp9xegnbMfg" %}
[Mimecast Allowlisting](/guides/getting-started/allowlisting-prventi-email-servers/mimecast-allowlisting)
{% endcontent-ref %}
# Google Workspace Allowlisting
Phishing attack simulations allowlist and configuration settings for Google Workspace
### Allowlist Prventi email
1. [Sign into](https://workspace.google.com) your Google Workspace admin console
2. Navigate to Apps > Google Workspace > Gmail
3. Navigate to Spam, phishing and malware
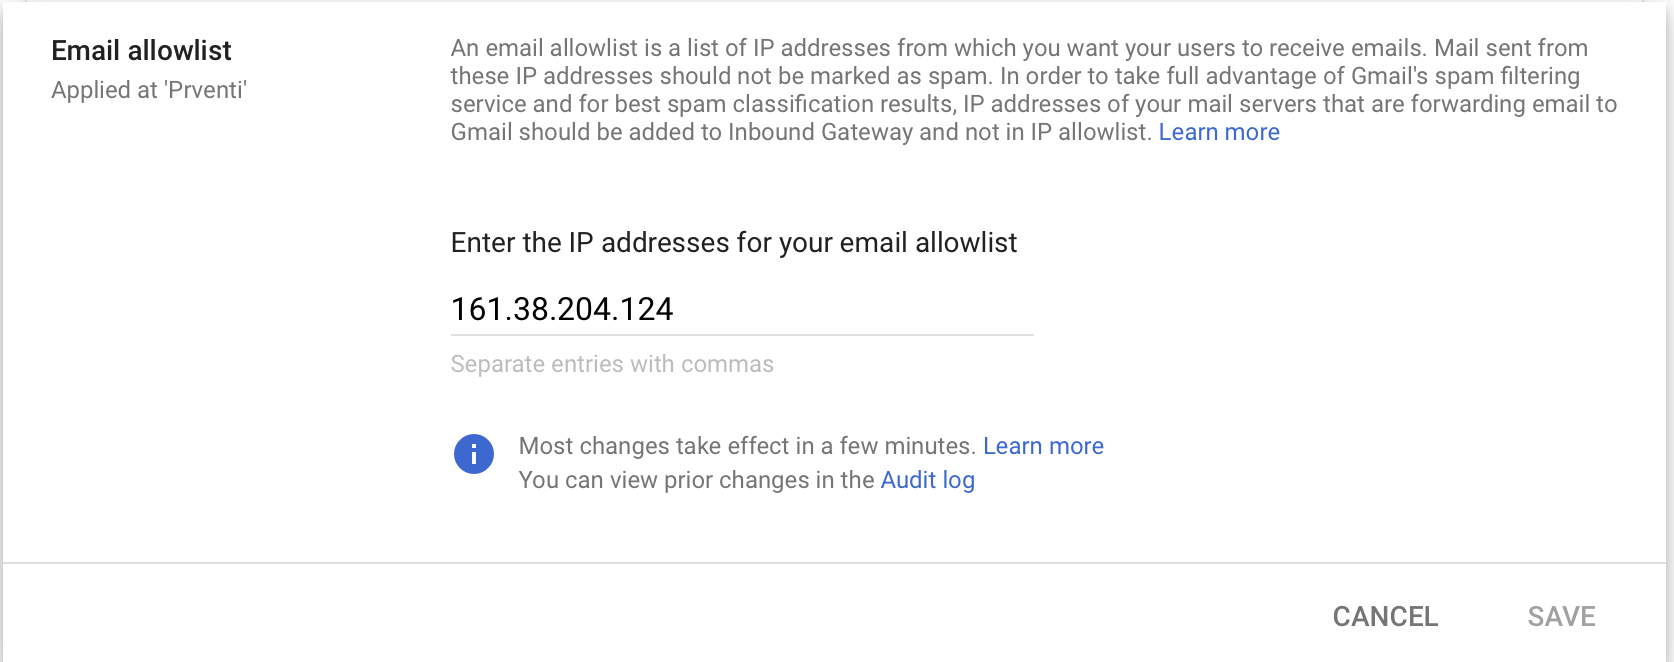
4. Edit the Email allowlist and add the Prventi IP addresses below and Save
| IP Address | Description |
| -------------- | --------------- |
| 161.38.204.124 | Phishing server |
### Add an inbound gateway
{% hint style="info" %}
After you allowlist an IP address, messages that come from that IP address won't be put in the spam label. However, users who receive email from that IP address are likely to still see a Gmail warning banner on those messages (for example, **This email looks suspicious**)
Adding the Prventi mail server as an inbound gateway can prevent the banner from showing.
{% endhint %}
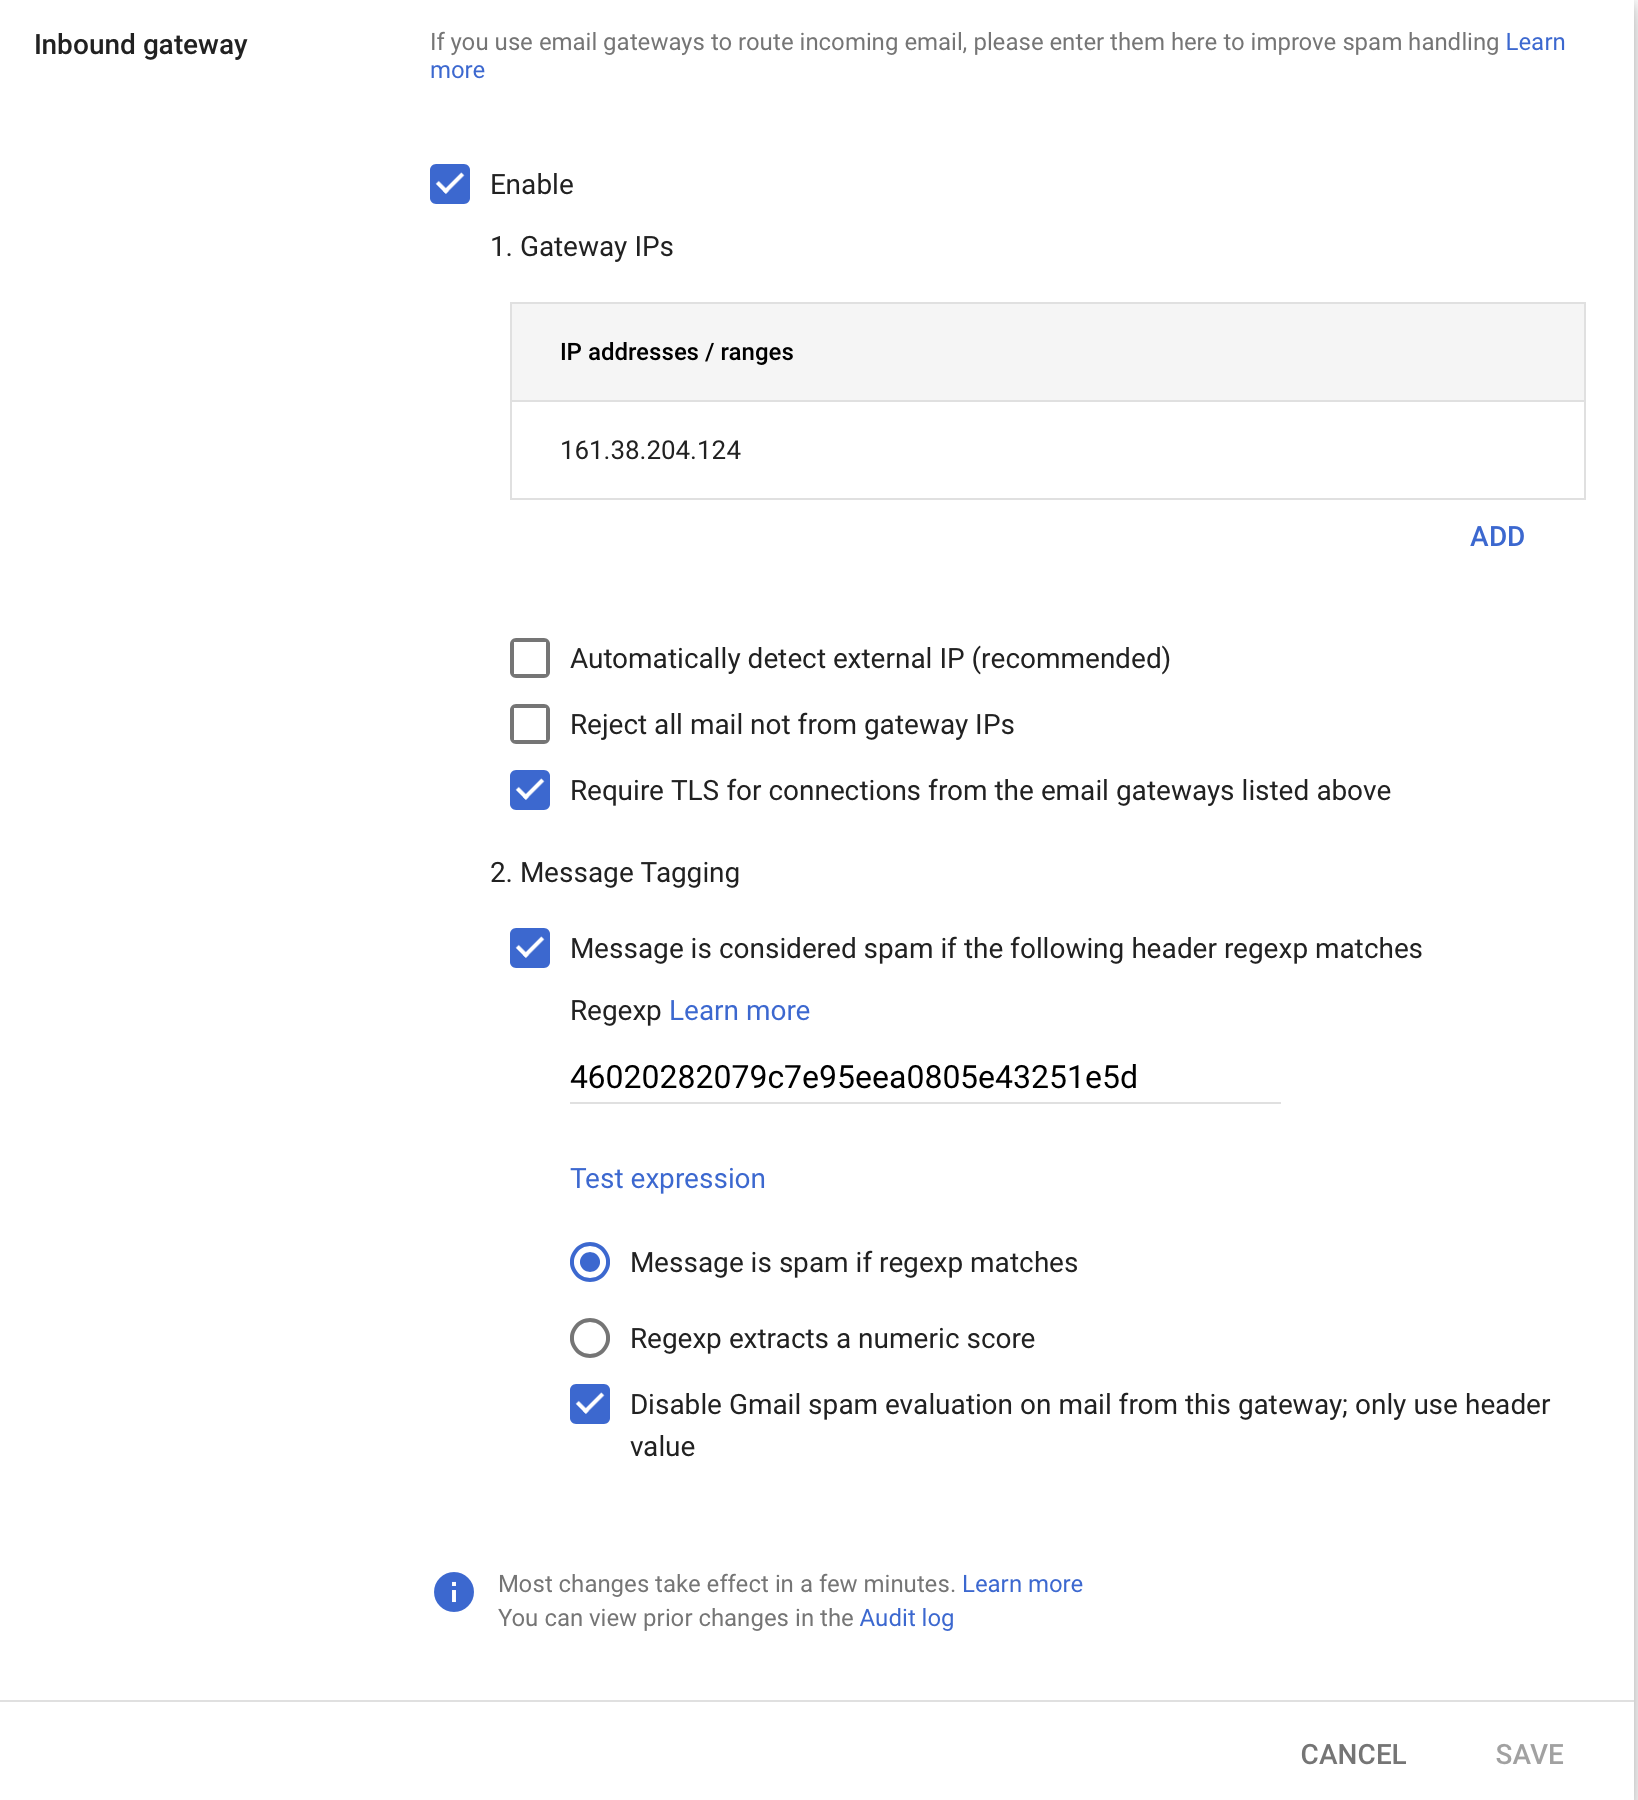
1. Navigate to Spam, phishing and malware
2. Enable `Inbound gateway`
3. Add the IP address from the table above
4. Deselect `Automatically detect external IP (recommended)`
5. Deselect `Reject all mail not from gateway IPs`
6. Select `Require TLS for connections from the email gateways listed above`
7. Select `Message is considered spam if the following header regexp matches`
8. Enter `46020282079c7e95eea0805e43251e5d` as the regex value
9. Select `Message is spam if regexp matches`
10. Disable `Gmail spam evaluation on mail from this gateway; only use header value`
# Microsoft Office 365 Allowlisting
{% hint style="info" %}
**Important**
To allow phishing URLs that are part of third-party attack simulation training, use the [advanced delivery configuration](https://learn.microsoft.com/en-us/microsoft-365/security/office-365-security/skip-filtering-phishing-simulations-sec-ops-mailboxes?view=o365-worldwide) to specify the URLs.
**Don't use the Tenant Allow/Block List.**
{% endhint %}
[Microsoft's secure by default feature](https://learn.microsoft.com/en-us/microsoft-365/security/office-365-security/secure-by-default?view=o365-worldwide) may affect the way your organization allowlists Prventi. Due to this change, you can allowlist Prventi using Microsoft's advanced delivery policies feature instead.
In this article, you will learn how to allowlist Prventi with the advanced delivery policy feature. Read more about [configuring the delivery of third-party phishing simulations to users](https://learn.microsoft.com/en-us/microsoft-365/security/office-365-security/skip-filtering-phishing-simulations-sec-ops-mailboxes?view=o365-worldwide#use-the-microsoft-365-defender-portal-to-configure-third-party-phishing-simulations-in-the-advanced-delivery-policy).
### How to Allowlist Prventi Using Advanced Delivery Policies
1. Navigate to the [Microsoft 365 Defender portal](https://security.microsoft.com/homepage)
2. Expand **Email and collaboration in the** menu
3. Select [Policies and Rules](https://security.microsoft.com/securitypoliciesandrules)
4. Select [Threat policies](https://security.microsoft.com/threatpolicy)
5. Select [Advanced delivery](https://security.microsoft.com/advanceddelivery)
6. Select the Phishing simulation tab at the top of the page
7. Select Edit
#### Add the following domains:
postman-pat.com, paymentnotifications.email, no-reply-sender.email
| Prventi Phishing Email Domains | Description |
| ------------------------------ | -------------------------- |
| postman-pat.com | Phishing simulation domain |
| paymentnotifications.email | Phishing simulation domain |
| no-reply-sender.email | Phishing simulation domain |
| sharepoitnonline.com | Phishing simulation domain |
#### Sending IP
| IP Address | Description |
| -------------- | -------------------------------- |
| 161.38.204.124 | Phishing simulation email server |
#### Simulation URLs to allow
| Phishing Website Domains | Description |
| ------------------------------- | ----------------------- |
| \*.securelogin.page/\* | Phishing website domain |
| \*.secure-online.store/\* | Phishing website domain |
| \*.securepayment.site/\* | Phishing website domain |
| \*.sharepoitnonline.com/\* | Phishing website domain |
| \*.compressed-download.zip/\* | Phishing website domain |
| \*.stable-release.zip/\* | Phishing website domain |
| \*.strictly-confidential.zip/\* | Phishing website domain |
| \*.final-1.zip/\* | Phishing website domain |
# Mimecast Allowlisting
**A Step-by-Step Guide for Prventi Customers**
At Prventi, we’re committed to helping you strengthen your organization’s cybersecurity through our security awareness training and simulated phishing tests. If your organization uses Mimecast as its email security solution, whitelisting Prventi is essential to ensure our simulated phishing emails and training notifications reach your users’ inboxes without being blocked or filtered.
This guide provides detailed instructions for configuring Mimecast policies to allow Prventi’s phishing simulations to function effectively. We’ve organized the steps in a recommended order to maximize success. If you encounter any issues, feel free to contact Prventi Support or consult Mimecast’s documentation for additional guidance.
#### Step 1: Create an Anti-Spoofing Policy Bypass
**Purpose:** This policy allows Prventi to send simulated phishing emails that appear to come from your own domain (e.g., for spear-phishing simulations), bypassing Mimecast’s anti-spoofing protections.
1. **Log in to Mimecast:** Access your Mimecast Administration Console.
2. **Navigate to Policies:** Click the **Administration** toolbar button, then select **Gateway | Policies**.
3. **Select Anti-Spoofing Policy:** From the list of policies, choose **Anti-Spoofing Bypass** and click **New Policy**.
4. **Configure Settings:**
* **Options:** Choose the appropriate anti-spoofing bypass settings (refer to Mimecast’s *Configuring an Anti-Spoofing Policy* guide for details).
* **Emails From:** Set to **External** (to allow Prventi’s external servers).
* **Emails To:** Set to **Internal Users** (or your specific domain).
* **Validity:** Ensure the policy is enabled and set an appropriate time frame (e.g., ongoing).
5. **Override the Policy:** Check the **Policy Override** box.
6. **Enter Source IP Ranges:** In the **Source IP Ranges** field, input Prventi’s IP ranges. Contact Prventi Support for the most up-to-date list of our IP addresses.
7. **Save the Policy:** Click **Save** to activate the policy.
{% hint style="info" %}
**Tip:** After saving, send a test phishing email to yourself or a small group to confirm it reaches the inbox as expected.
{% endhint %}
***
#### Step 2: Set Up a Permitted Senders Policy
**Purpose:** This policy ensures Prventi’s phishing and training-related emails are permitted through Mimecast’s filters, avoiding spam or junk folders.
{% hint style="danger" %} **Create a new Permitted Sender policy; do not edit the default**
{% endhint %}
1. **Access Policies:** In the Mimecast Administration Console, go to **Gateway | Policies**.
2. **Create a New Policy:** Select **Permitted Senders** from the policy list and click **New Policy**.
3. **Configure Settings:**
* **Options:** Select settings to permit sender emails (see Mimecast’s *Configuring a Permitted Senders Policy* for specifics).
* **Emails From:** Set to **External**.
* **Emails To:** Set to **Internal Users**.
* **Validity:** Enable the policy and set the desired duration.
4. **Override the Policy:** Check the **Policy Override** box.
5. **Add Source IP Ranges:** Enter Prventi’s IP ranges in the **Source IP Ranges** field (available from Prventi Support).
6. **Save the Policy:** Click **Save** to apply the changes.
{% hint style="info" %}
**Tip:** Test this policy with a small campaign to verify that emails arrive without interference.
{% endhint %}
***
#### Step 3: Configure an Attachment Management Bypass Policy
**Purpose:** If your phishing simulations include attachments (e.g., fake PDFs or documents), this policy prevents Mimecast from stripping them, ensuring accurate test results.
1. **Go to Policies:** In the Mimecast Administration Console, select **Gateway | Policies**.
2. **Choose Attachment Policy:** Select **Attachment Management Bypass** from the list and click **New Policy**.
3. **Set Policy Details:**
* **Options:** Adjust settings to bypass attachment filtering (refer to Mimecast’s *Configuring Attachment Management Bypass Policies*).
* **Emails From:** Set to **External**.
* **Emails To:** Set to **Internal Users**.
* **Validity:** Enable the policy as needed.
4. **Override the Policy:** Check the **Policy Override** box.
5. **Input Source IP Ranges:** Add Prventi’s IP ranges in the **Source IP Ranges** field.
6. **Save the Policy:** Click **Save** to finalize.
{% hint style="info" %}
**Tip:** Send a test email with an attachment to confirm it arrives intact. Stripped attachments can skew your phishing test results.
{% endhint %}
***
#### Step 4: Optional – Prevent URL Rewriting (If Needed)
**Purpose:** Mimecast may rewrite URLs in emails, which can break phishing simulation links. This step ensures Prventi’s links remain functional.
1. **Navigate to URL Policies:** In the Mimecast Administration Console, go to **Gateway | Policies**.
2. **Select URL Protection Bypass:** Choose **URL Protection Bypass** and click **New Policy**.
3. **Configure Settings:**
* Set to bypass URL rewriting for Prventi’s domains or IPs.
* Contact Prventi Support for our specific domains if needed.
4. **Save the Policy:** Apply and test to ensure links work as intended.
{% hint style="info" %}
**Note:** This step is optional and depends on whether URL rewriting affects your tests.
{% endhint %}
***
#### Testing Your Configuration
Once you’ve set up these policies, we recommend running a small test campaign:
* Create a phishing simulation in your Prventi dashboard targeting yourself or a select group.
* Verify that emails arrive in inboxes, attachments remain intact, and links function correctly.
* Adjust policies as needed based on the results.
# Send a delivery test email
Welcome to the crucial step of ensuring effective email delivery in your Prventi security awareness training program. After allowlisting our email servers with your provider, it's essential to conduct a delivery test email. This process confirms that Prventi’s phishing simulation and training emails will successfully reach your users. Here’s how to do it and why it’s important.
#### Why Send a Delivery Test Email?
* **Confirm Successful Configuration:** Ensure that the allowlisting process has been correctly implemented and that emails from Prventi are not being blocked or sent to spam.
* **Avoid Disruptions in Training:** Effective delivery is key to the success of your cybersecurity training program. Testing confirms that all users will receive the necessary training content without issues.
* **Troubleshoot Early:** Identify and resolve any delivery issues before rolling out your phishing campaigns and training modules.
#### How to Conduct the Delivery Test Email
1. **Access the Delivery Test Section:**
* Log in to your Prventi account.
* Navigate to the ‘Email Delivery Test’ section within your dashboard.
2. **Initiate the Test:**
* Follow the instructions to send a test email from Prventi’s system to a few selected email addresses within your organization.
* It’s recommended to choose addresses across different departments or roles to ensure comprehensive testing.
3. **Check for Email Receipt:**
* Verify that the test email is received in the inboxes of the selected addresses.
* Ask the recipients to check their spam or junk folders if the email is not found in the inbox.
4. **Confirm Delivery:**
* Once you have confirmation that the test email was successfully received, report the successful delivery in the Prventi platform.
* If there are issues, refer to troubleshooting tips provided in Prventi, or contact our support team.
#### Troubleshooting Delivery Issues
* **Check Spam/Junk Folders:** Ensure the test email hasn’t been mistakenly marked as spam.
* **Review Allowlisting Settings:** Revisit your email provider's settings to confirm that Prventi’s email servers are correctly allowlisted.
* **Consult IT Department:** If issues persist, consult your IT team to investigate potential barriers in your email system.
#### Need Help?
If you encounter any challenges during the domain verification process or have questions about modifying your DNS settings, our support team is here to assist you. [Contact our support](https://www.prventi.com/support) for guidance and support.
Thank you for taking this important step in setting up your organization on Prventi. Once your domain is verified, you're all set to launch your baseline phishing campaign and strengthen your organisation's defence against cyber threats.
# Start a baseline phishing campaign
Welcome to the Baseline Phishing Campaign section of Prventi! This campaign is a crucial first step in assessing and enhancing your organization's cybersecurity awareness and preparedness. Below, we explain the purpose, process, and importance of running a Baseline Phishing Campaign.
#### What is a Baseline Phishing Campaign?
A Baseline Phishing Campaign involves sending simulated phishing emails to the employees within your organization. The purpose of these simulations is not to trick your employees, but to assess the current level of awareness and preparedness against real-life phishing attacks. This initial assessment establishes a baseline - a starting point from which progress and improvement will be measured.
#### Objectives of the Baseline Phishing Campaign
* **Assess Current Vulnerability:** Determine how susceptible your organization is to phishing attacks.
* **Identify Areas for Improvement:** Highlight which areas or which groups within your organization need more training.
* **Measure Progress:** Provide a benchmark against which the effectiveness of subsequent training can be measured.
#### How Does the Baseline Campaign Work?
1. **Planning the Campaign:**
* Select the target group within your organization for the campaign.
* Choose from a range of simulated phishing email templates that mimic real-world phishing scenarios.
2. **Launching the Campaign:**
* The selected phishing simulations are sent to the employees over a designated period.
* These emails are designed to be safe and do not harm or access personal data.
3. **Monitoring and Collecting Data:**
* Track how recipients interact with the simulation emails - who opens them, clicks on links, or provides information.
* Collect data anonymously to respect privacy and ensure unbiased results.
4. **Analyzing Results:**
* Post-campaign, we provide an analysis of the campaign's outcomes.
* Understand the susceptibility rate and identify patterns or trends in how employees responded.
#### After the Baseline Campaign
* **Customized Training:** Based on the results, you can tailor subsequent cybersecurity training programs to address specific vulnerabilities or gaps in knowledge.
* **Follow-up Campaigns:** Run additional phishing simulations periodically to measure improvement and keep awareness high.
#### Need Help?
If you encounter any challenges during the domain verification process or have questions about modifying your DNS settings, our support team is here to assist you. [Contact our support](https://www.prventi.com/support) for guidance and support.
Thank you for taking this important step in setting up your organization on Prventi. Once your domain is verified, you're all set to launch your baseline phishing campaign and strengthen your organisation's defence against cyber threats.
# Invite team members to Prventi
For optimal success with Prventi's platform, it's imperative that key members in your organisation, especially decision-makers, are aligned with the objectives, benefits, and framework of the security awareness training program.
**Best Practice Alert!** Before you kickstart the first training campaigns for the entire organisation, it's wise to loop everyone in.
To make this step easier, we've drafted a sample email below that you can reference. Remember to adjust placeholders and context to fit your organisation's unique approach to security training.
```
Subject: Upcoming Invitation: Join Us on the Prventi Platform!
Dear [Employee's First Name / Team],
We are excited to announce that we have partnered with Prventi, a leading platform dedicated to strengthening our organisation's cybersecurity awareness and practices. This partnership is part of our ongoing commitment to ensuring that we remain secure in an ever-evolving digital landscape.
What to Expect?
In the coming days, you will receive an email invitation from the Prventi platform. This email will provide you with instructions on how to join our organisation's group on Prventi, where you will have access to various resources, training modules, and security awareness programs tailored for us.
Why Prventi?
Cyber threats are continually evolving, and it's crucial for every member of our team to be knowledgeable and vigilant. Prventi offers an intuitive platform that not only educates but also equips us with the skills to recognize and counteract potential threats. By joining, you'll be fortifying our collective defense against cyber threats.
What Should You Do?
Look Out for the Invitation: The email will be coming from no-reply@mailer.prventi.com. Please ensure it doesn't get caught in your spam or junk folder.
Act Promptly: Once you receive the invitation, please follow the instructions to set up your Prventi account as soon as possible.
Stay Vigilant: Be wary of any suspicious emails. If you're uncertain about the legitimacy of the Prventi invitation or any other emails, please reach out to our IT department at [Company IT Support Email].
Your participation and commitment to our cybersecurity initiatives are vital. We encourage everyone to take full advantage of the resources Prventi offers. Let's work together to bolster our defenses and foster a culture of cybersecurity awareness.
Thank you for your attention to this important matter, and we look forward to our collective journey toward enhanced cyber safety with Prventi!
Warm regards,
[Your Name / Your Position]
[Company Name]
[Company Contact Information]
```